Post Deployment Validations
-
Check Components in Kubernetes:
- Ensure all Yeedu components are successfully deployed in the Kubernetes cluster.
- Verify the status and health of each component, including but not limited to:
- Deployment pods
- Services
- ConfigMaps
- Secrets
- Use Kubernetes commands such as
kubectl get pods,kubectl get services, etc., to inspect the status of the deployed components.
-
Access UI from Browser:
- Open a web browser.
- Navigate to the URLs associated with the Yeedu UI components, such as:
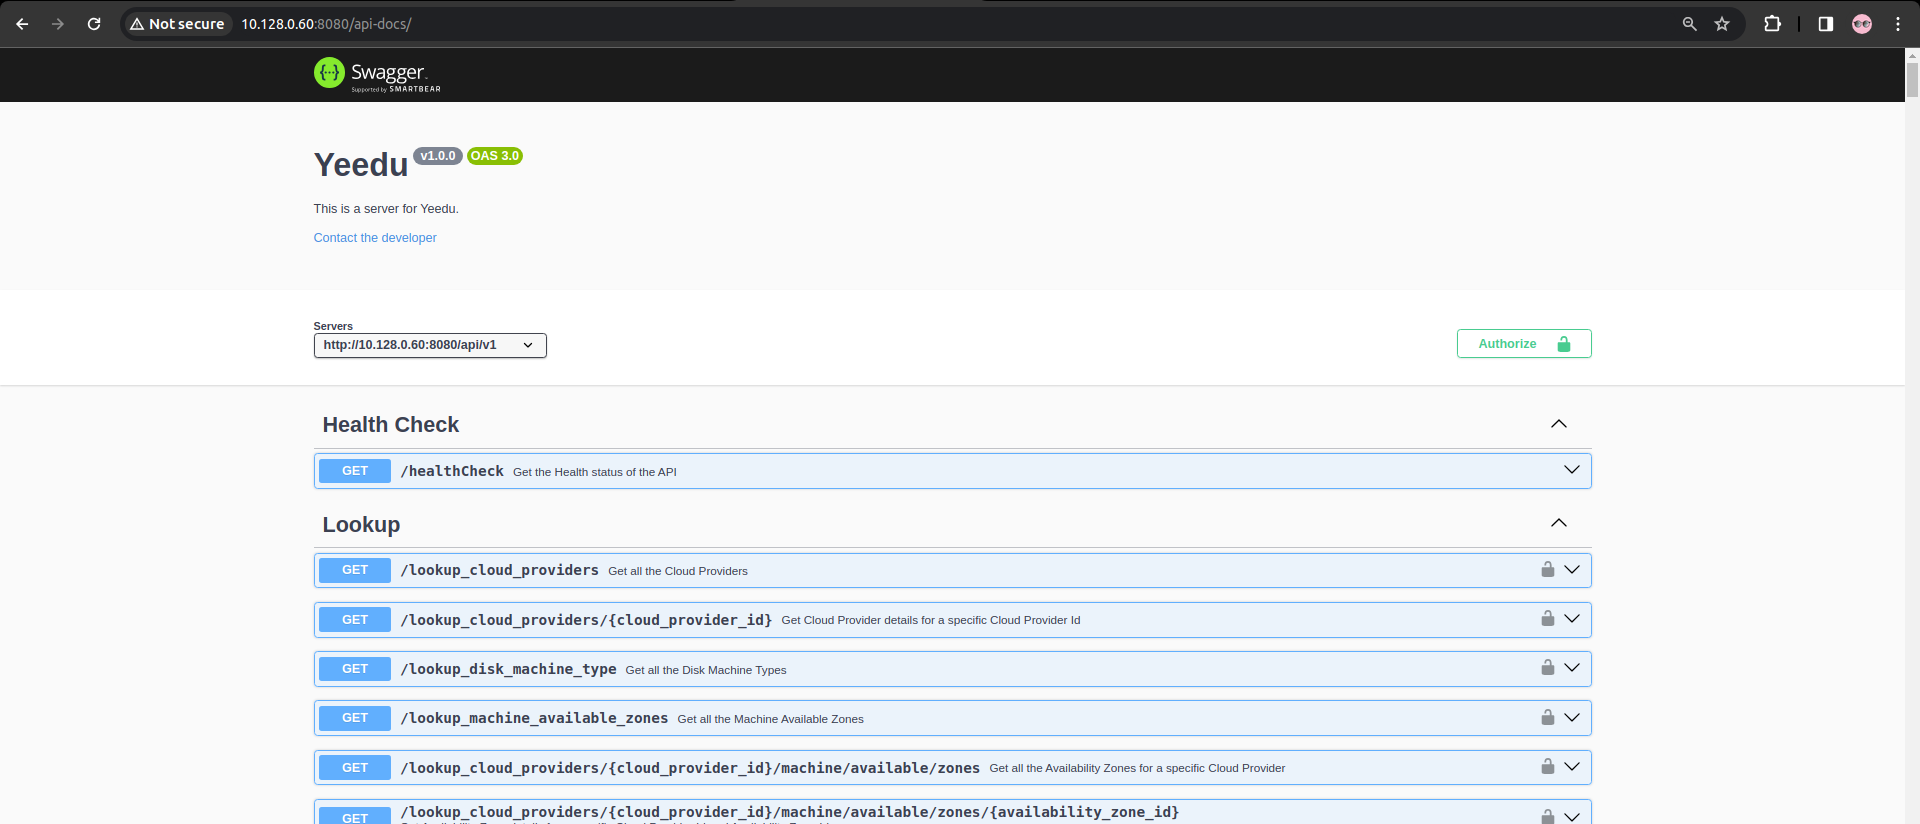
- Yeedu REST API
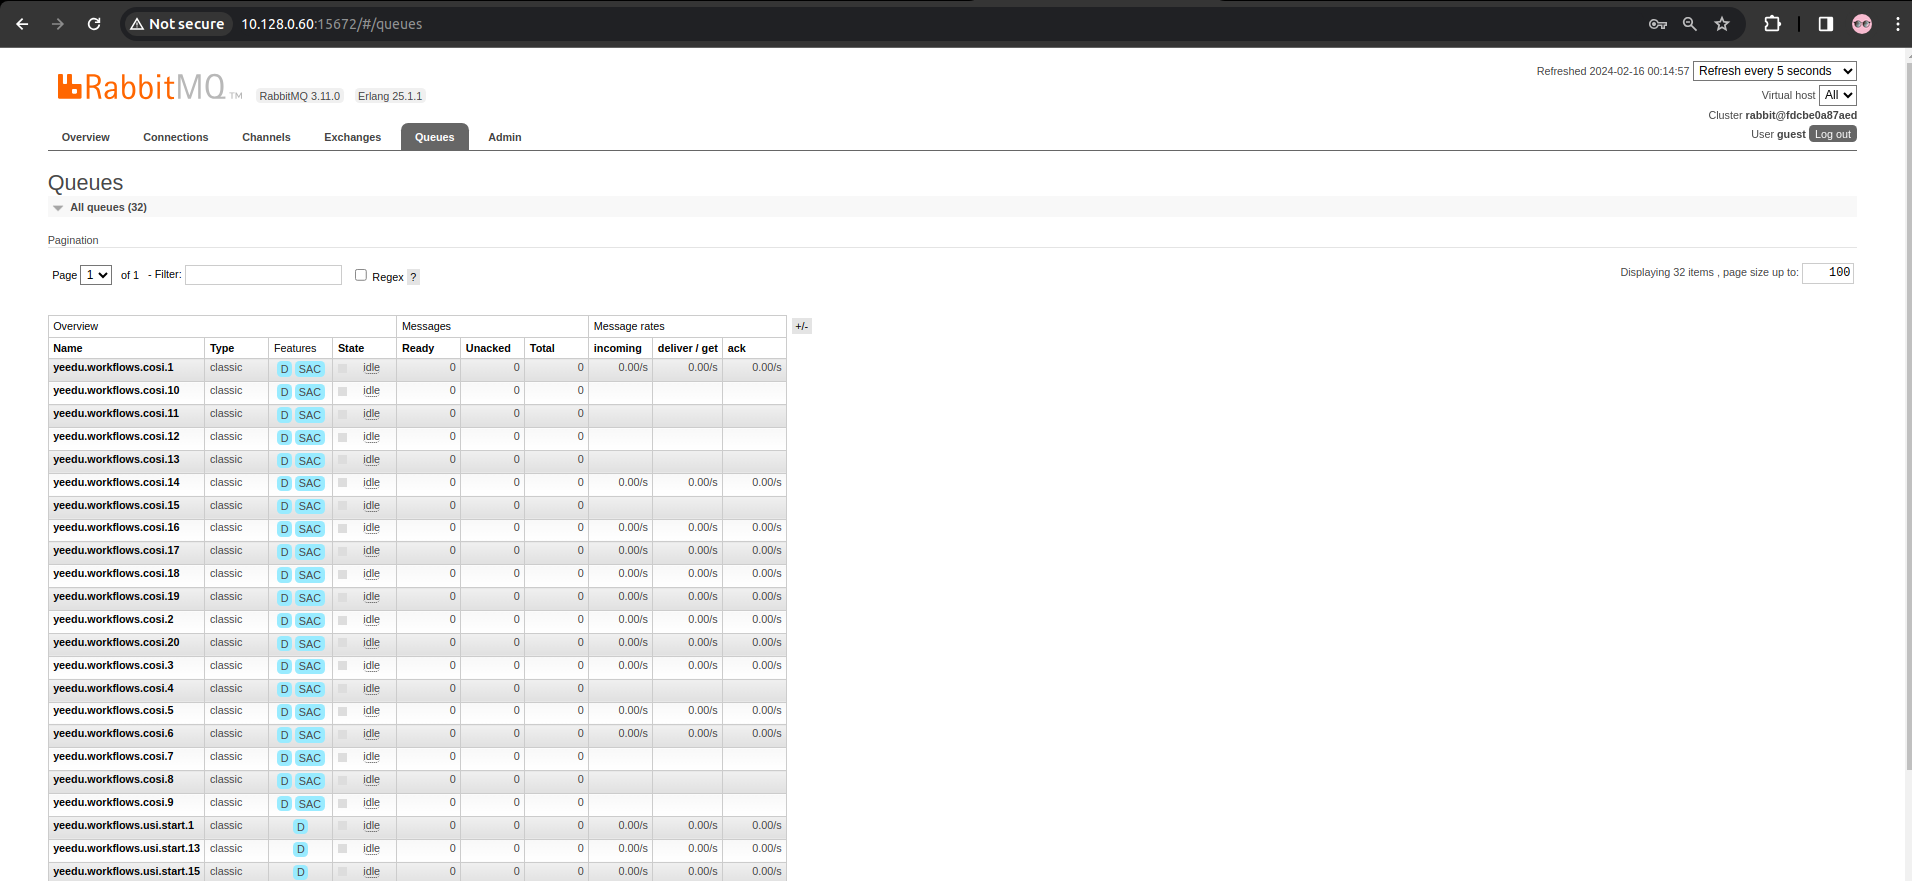
- RabbitMQ UI
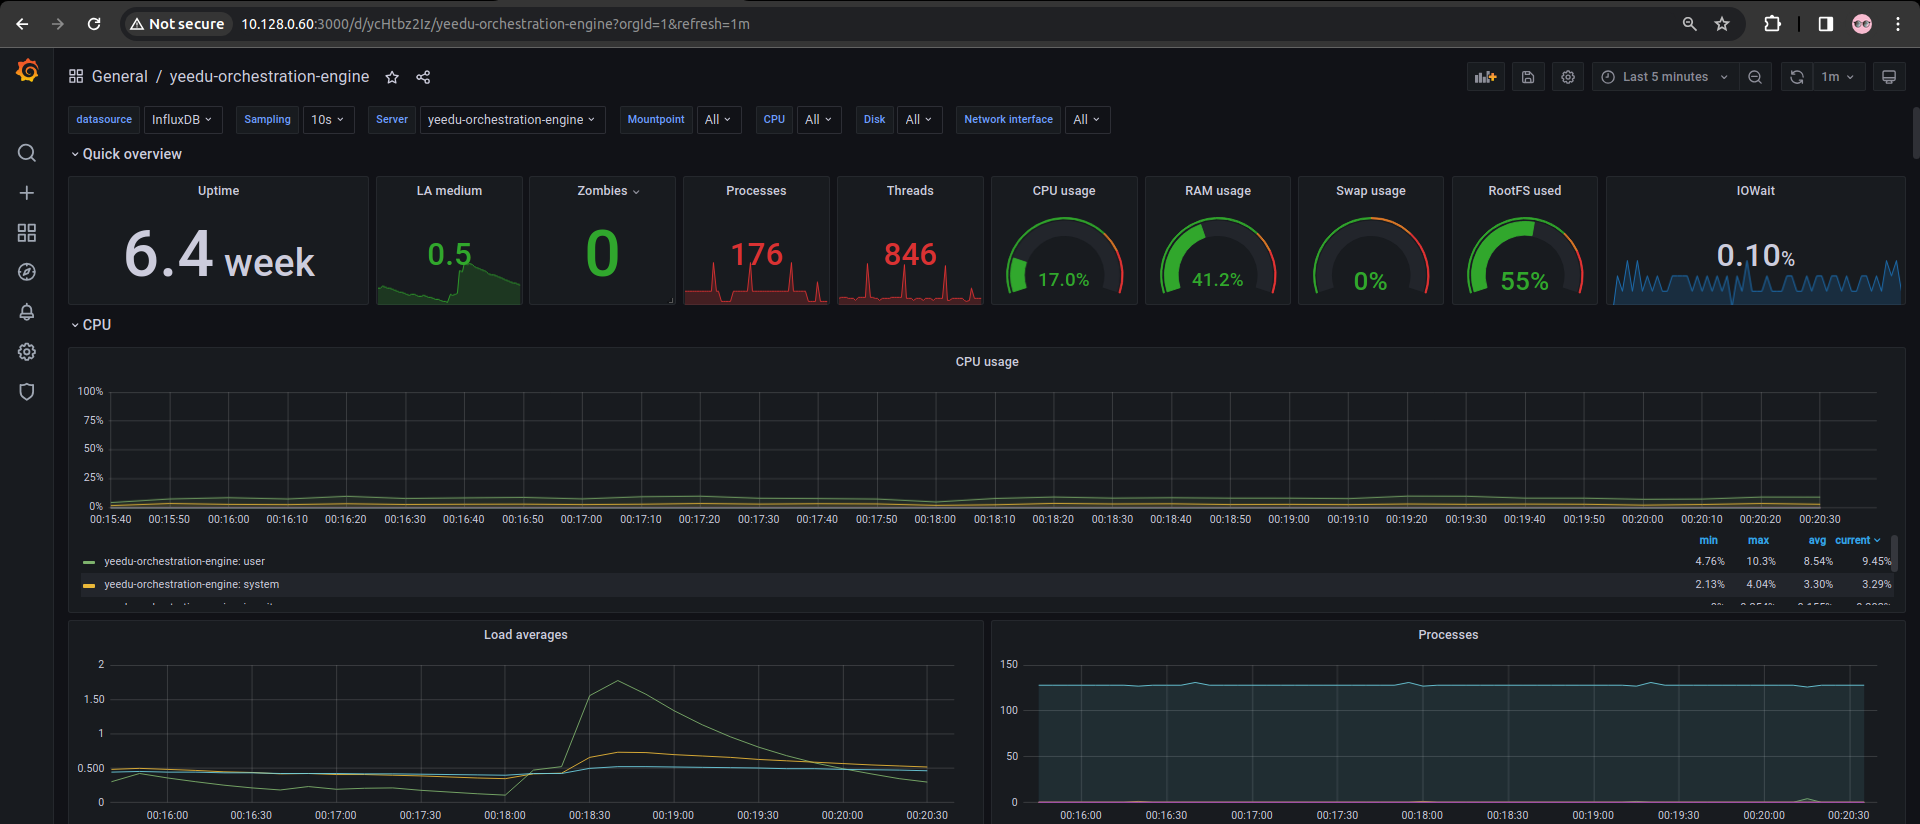
- Grafana
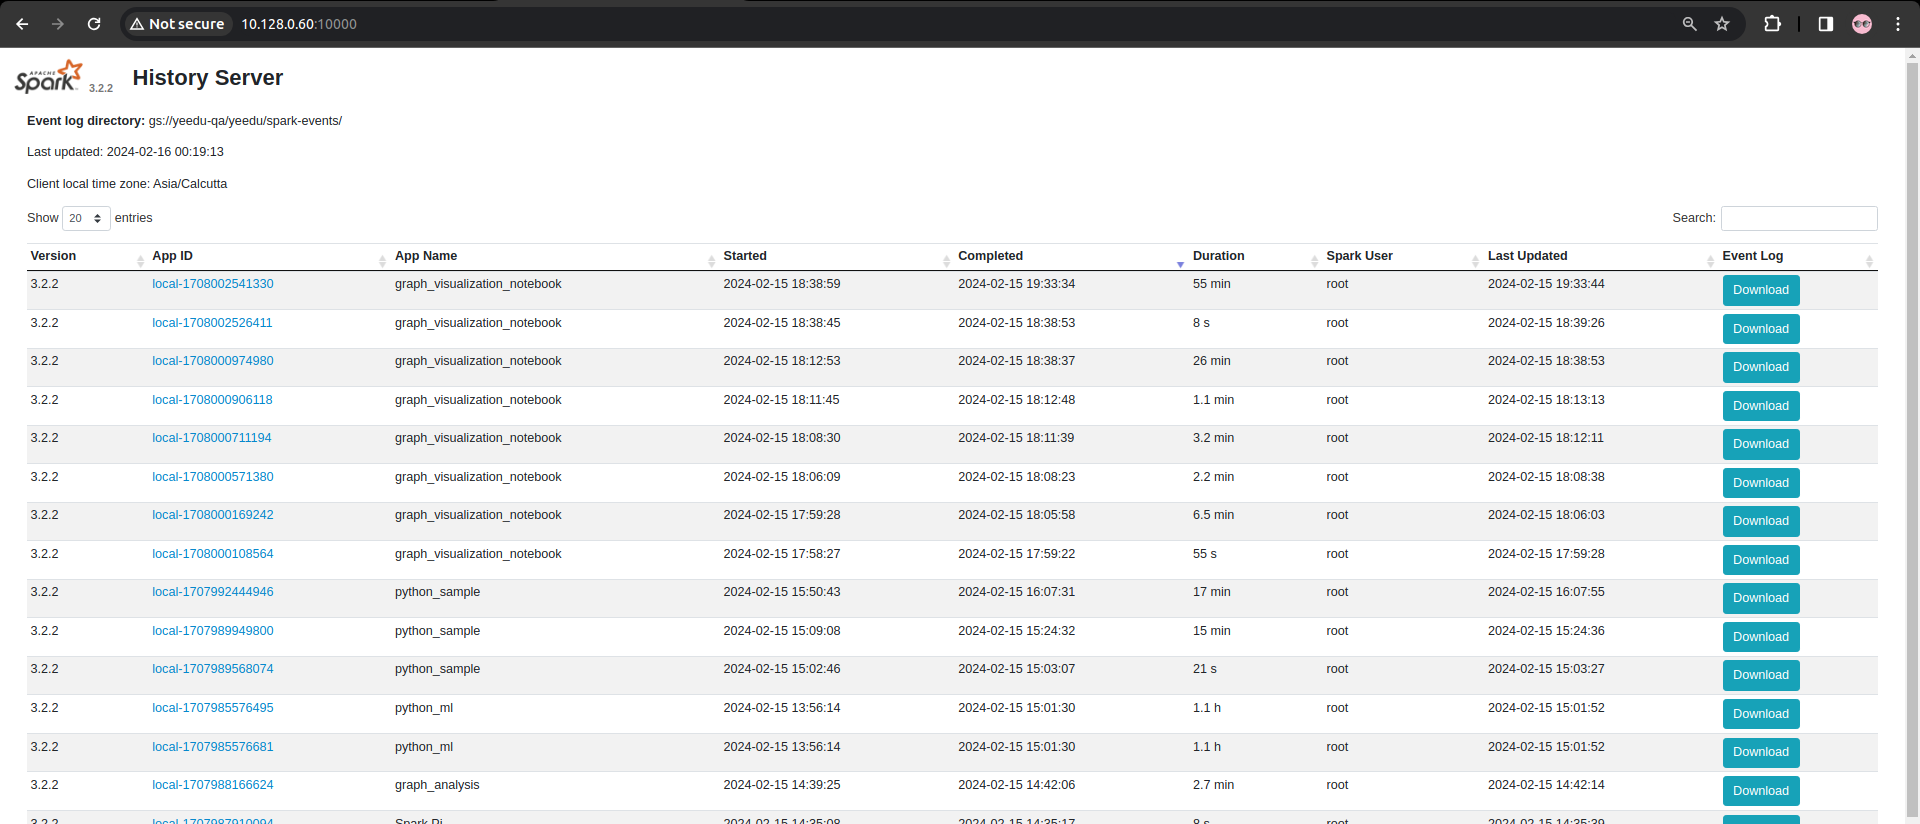
- Ensure that the UIs are accessible and responsive, indicating successful deployment and availability of Yeedu Runtime services.
1. Components in Kubernetes
Validate the created components such as configmaps, services, Persistent Volume Claims, Persistent Volumes, Deployments, Pods, Ingress, Statefulsets. The outcome should depict something as shown below.
1.1. ConfigMaps
The following should be the output when you list configmaps:
$ kubectl get configmaps -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
NAME                                                DATA   AGE
ingress-nginx-controller                            5      23m
kube-root-ca.crt                                    1      31d
tcp-services                                        9      23m
yeedu-aws-retention-json                            1      4m10s
yeedu-azure-retention-json                          1      4m9s
yeedu-cloud-credential-json                         1      4m12s
yeedu-core-ingress-controller                       1      16d
yeedu-docker-registry-credential-json               1      4m11s
yeedu-gcp-retention-json                            1      4m8s
yeedu-grafana-config-files                          1      3m56s
yeedu-grafana-config-files-all                      1      4m1s
yeedu-grafana-config-files-grafana-home-dashboard   1      4m
yeedu-grafana-config-files-influxdb                 1      4m4s
yeedu-grafana-config-files-ini                      1      3m59s
yeedu-grafana-config-files-ldap                     1      4m3s
yeedu-ldap-files                                    1      4m7s
yeedu-rabbitmq-files                                2      4m6s
yeedu-rabbitmq3-plugins-conf                        1      3m1s
yeedu-rabbitmq3-server-conf                         2      3m1s
yeedu-redis-files                                   2      4m5s
yeedu-telegraf-config-files                         1      3m55s
1.2. Services
You should be seeing the below output when you list services
$ kubectl get svc -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
NAME                                                           TYPE           CLUSTER-IP     EXTERNAL-IP   PORT(S)                                                                                                                                                              AGE
ingress-nginx-controller                                       LoadBalancer   10.0.226.237   10.4.6.156    80:30593/TCP,443:30796/TCP,3000:32196/TCP,10000:31674/TCP,5432:31148/TCP,389:31589/TCP,6379:31539/TCP,5672:30978/TCP,15672:32195/TCP,8080:31028/TCP,8086:31665/TCP   25m
ingress-nginx-controller-admission                             ClusterIP      10.0.19.225    <none>        443/TCP                                                                                                                                                              25m
yeedu-grafana-clusterip                                        ClusterIP      10.0.120.102   <none>        3000/TCP                                                                                                                                                             2m57s
yeedu-history-server-clusterip                                 ClusterIP      10.0.183.238   <none>        10000/TCP                                                                                                                                                            2m56s
yeedu-influxdb-clusterip                                       ClusterIP      10.0.190.71    <none>        8086/TCP                                                                                                                                                             2m55s
yeedu-ldap-clusterip                                           ClusterIP      10.0.118.52    <none>        389/TCP                                                                                                                                                              5m12s
yeedu-metadata-db-clusterip                                    ClusterIP      10.0.201.94    <none>        5432/TCP                                                                                                                                                             5m13s
yeedu-rabbitmq3                                                ClusterIP      10.0.144.204   <none>        5672/TCP,15672/TCP,15692/TCP                                                                                                                                         4m36s
yeedu-rabbitmq3-nodes                                          ClusterIP      None           <none>        4369/TCP,25672/TCP                                                                                                                                                   4m36s
yeedu-rabbitmq3-rabbitmq-messaging-topology-operator-webhook   ClusterIP      10.0.89.93     <none>        443/TCP                                                                                                                                                              4m54s
yeedu-redis-clusterip                                          ClusterIP      10.0.231.179   <none>        6379/TCP                                                                                                                                                             5m13s
yeedu-restapi-clusterip                                        ClusterIP      10.0.46.19     <none>        8080/TCP                                                                                                                                                             2m55s
1.3. Persistent Volume Claims
You'll see the below output when you list pvc
$ kubectl get pvc -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
NAME                                   STATUS   VOLUME                                     CAPACITY   ACCESS MODES   STORAGECLASS          AGE
persistence-yeedu-rabbitmq3-server-0   Bound    pvc-13b9c5c5-a07b-4c92-b40b-6439d6a55793   20Gi       RWO            yeedu-storage-class   5m13s
persistence-yeedu-rabbitmq3-server-1   Bound    pvc-6a46ff4c-3afe-480b-a878-3b1654e3bfcd   20Gi       RWO            yeedu-storage-class   5m13s
persistence-yeedu-rabbitmq3-server-2   Bound    pvc-d15ab56e-67dc-440b-82f4-74fe114dbd49   20Gi       RWO            yeedu-storage-class   5m13s
yeedu-influxdb-volume                  Bound    pvc-0742419c-7a7c-4853-b5af-93909c72136d   200Gi      RWO            yeedu-storage-class   3m34s
yeedu-ldap-pvc                         Bound    pvc-14a45bb0-c7bd-4924-bdc0-06b1db854a29   10Gi       RWO            yeedu-storage-class   5m51s
yeedu-ldap-slapd-pvc                   Bound    pvc-ee59d86c-97fb-4b99-8b3b-aeb309773faa   10Gi       RWO            yeedu-storage-class   5m51s
yeedu-metadata-db-pvc                  Bound    pvc-3feee8a7-67c6-4f0a-be18-ec814b4bd101   20Gi       RWO            yeedu-storage-class   5m51s
yeedu-reactors-logs-volume             Bound    pvc-b718c992-9ef7-4c0d-8b45-1968ef8e6918   100Gi      RWO            yeedu-storage-class   3m35s
yeedu-redis-volume                     Bound    pvc-9a1352cd-a588-455d-894d-0807c5d95c88   50Gi       RWO            yeedu-storage-class   5m51s
1.4. Persistent Volumes
You should be seeing the below output when you list pv
$ kubectl get pv -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
NAME                                       CAPACITY   ACCESS MODES   RECLAIM POLICY   STATUS   CLAIM                                        STORAGECLASS          REASON   AGE
pvc-0742419c-7a7c-4853-b5af-93909c72136d   200Gi      RWO            Delete           Bound    yeedu/yeedu-influxdb-volume                  yeedu-storage-class            3m57s
pvc-13b9c5c5-a07b-4c92-b40b-6439d6a55793   20Gi       RWO            Delete           Bound    yeedu/persistence-yeedu-rabbitmq3-server-0   yeedu-storage-class            5m37s
pvc-14a45bb0-c7bd-4924-bdc0-06b1db854a29   10Gi       RWO            Delete           Bound    yeedu/yeedu-ldap-pvc                         yeedu-storage-class            6m14s
pvc-3feee8a7-67c6-4f0a-be18-ec814b4bd101   20Gi       RWO            Delete           Bound    yeedu/yeedu-metadata-db-pvc                  yeedu-storage-class            6m15s
pvc-6a46ff4c-3afe-480b-a878-3b1654e3bfcd   20Gi       RWO            Delete           Bound    yeedu/persistence-yeedu-rabbitmq3-server-1   yeedu-storage-class            5m37s
pvc-9a1352cd-a588-455d-894d-0807c5d95c88   50Gi       RWO            Delete           Bound    yeedu/yeedu-redis-volume                     yeedu-storage-class            6m15s
pvc-b718c992-9ef7-4c0d-8b45-1968ef8e6918   100Gi      RWO            Delete           Bound    yeedu/yeedu-reactors-logs-volume             yeedu-storage-class            3m58s
pvc-d15ab56e-67dc-440b-82f4-74fe114dbd49   20Gi       RWO            Delete           Bound    yeedu/persistence-yeedu-rabbitmq3-server-2   yeedu-storage-class            5m37s
pvc-ee59d86c-97fb-4b99-8b3b-aeb309773faa   10Gi       RWO            Delete           Bound    yeedu/yeedu-ldap-slapd-pvc                   yeedu-storage-class            6m14s
1.5. Deployments
kubectl get deployment -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
Every workload name is prefixed with the Helm release name it belongs to. We install Yeedu as two Helm releases, yeedu-tps (third-party services) and yeedu-ycs (Yeedu core services), plus the ingress controller. The Deployments our current charts create are:
| Deployment | Release | Created when |
|---|---|---|
<tps-release>-postgres | yeedu-tps | YEEDU_DEPLOY_LOCAL_POSTGRES=true |
<tps-release>-ldap | yeedu-tps | YEEDU_DEPLOY_LOCAL_LDAP=true |
| RabbitMQ cluster operator | yeedu-tps | Always (Bitnami rabbitmq-cluster-operator subchart) |
| RabbitMQ messaging topology operator | yeedu-tps | Always (Bitnami rabbitmq-cluster-operator subchart) |
<ycs-release>-restapi | yeedu-ycs | Always |
<ycs-release>-ui | yeedu-ycs | Always |
<ycs-release>-vault | yeedu-ycs | Always |
<ycs-release>-history-server | yeedu-ycs | Always |
<ycs-release>-reactors-monitor | yeedu-ycs | Always |
<ycs-release>-grafana | yeedu-ycs | YEEDU_ENABLE_GRAFANA_MONTORING=true |
<ycs-release>-influxdb | yeedu-ycs | YEEDU_ENABLE_GRAFANA_MONTORING=true |
<ycs-release>-functions-scheduler | yeedu-ycs | Always |
<ycs-release>-functions-proxy | yeedu-ycs | Always |
<ycs-release>-functions-celery | yeedu-ycs | Always |
| Apache Airflow deployments (subchart) | yeedu-ycs | YEEDU_ENABLE_SCHEDULER=true |
ingress-nginx-controller | ingress | Always |
yeedu-reactors-cosi is a StatefulSet, not a Deployment, and log synchronisation runs as the yeedu-reactors-logs-sync container inside that StatefulSet's pods. There's no separate log-sync Deployment.
1.6. Pods
kubectl get pods -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
Expect one pod per Deployment replica listed above, the StatefulSet pods listed in section 1.7, and a number of completed one-shot Jobs from the install (ingress admission jobs, the Yeedu init job, and the ingress/DNS patch jobs). All long-running pods should reach Running with all containers ready; the Jobs should show Completed.
1.7. Statefulsets
kubectl get statefulset -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
Our current charts create:
| StatefulSet | Release | Notes |
|---|---|---|
<ycs-release>-reactors-cosi | yeedu-ycs | Runs the reactors container and the log-sync container |
| RabbitMQ cluster server | yeedu-tps | Created by the RabbitmqCluster custom resource, 3 replicas |
| Redis master and replicas | yeedu-tps | Bitnami Redis subchart, replica.replicaCount: 3 |
1.8. Secrets
kubectl get secret -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
Expect at minimum:
yeedu-certs(kubernetes.io/tls): the ingress certificate built fromssl/yeedu.crtandssl/yeedu.keyyeedu-image-pull-secret(kubernetes.io/dockerconfigjson): the container registry credentials- The RabbitMQ default-user and Erlang-cookie secrets, and the messaging-topology-operator webhook certificate
- The ingress admission webhook secret
- One
sh.helm.release.v1.<release>.v<n>secret per Helm release. With the current layout that isyeedu-tps,yeedu-ycsand the ingress release
You can list the Helm releases directly instead:
helm list -n $YEEDU_SYSTEM_KUBERNETES_NAMESPACE
1.9. Ingress Services
You'll see the below output when you list ingress services
$ kubectl get svc -n yeedu
NAME                                 TYPE           CLUSTER-IP     EXTERNAL-IP   PORT(S)                                                                                                                                                              AGE
ingress-nginx-controller             LoadBalancer   10.0.226.237   10.4.6.156    80:30593/TCP,443:30796/TCP,3000:32196/TCP,10000:31674/TCP,5432:31148/TCP,389:31589/TCP,6379:31539/TCP,5672:30978/TCP,15672:32195/TCP,8080:31028/TCP,8086:31665/TCP   6m35s
ingress-nginx-controller-admission   ClusterIP      10.0.19.225    <none>        443/TCP                                                                                                                                                              6m35s
1.10. Ingress Pods
You should be seeing the below output when you list Ingress Pods
$ kubectl get pods -n yeedu
NAME                                        READY   STATUS      RESTARTS   AGE
ingress-nginx-admission-create-fzvnz        0/1     Completed   0          5m25s
ingress-nginx-admission-patch-g565f         0/1     Completed   0          5m25s
ingress-nginx-controller-6fdbb469b9-nv8bh   1/1     Running     0          5m26s
2. Access from Browser
2.1. RabbitMQ
2.2. History Server
2.3. Grafana
2.4. Rest-API